Security expertise, direct and independent
I'm Chirag Arora — a Bengaluru-based cybersecurity consultant. Businesses bring me in to look at their systems the way a determined attacker would, and to translate what I find into decisions they can act on.
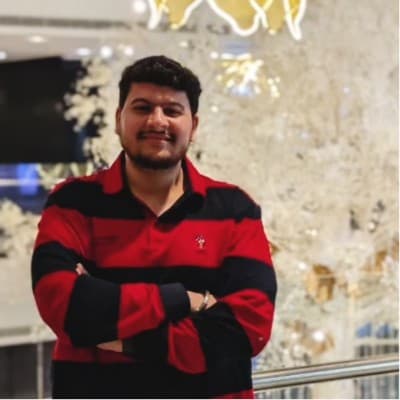
Security is a decision problem before it's a technical one. A vulnerability report is only useful if someone acts on it. Over four years across consulting engagements in Finance, Healthcare, and Government, that has been the throughline — running the full VAPT and vulnerability-management lifecycle, then making sure the result lands as a decision a client can act on, not a PDF they file away.
That means going deep technically — network, OS configuration, and web application testing, much of it inside PCI DSS-scoped, on-site engagements — and translating it upward into executive summaries and risk reports that hold up in a room with people who don't read CVE identifiers for a living. It also means running the engagement itself: planning, resourcing, and governance across concurrent assessments, not just the testing inside them.
Every engagement is grounded in explicit, documented authorization and a clearly agreed scope. Confidentiality is non-negotiable, and I'm glad to work under an NDA.
Areas of expertise
- Vulnerability Assessment & Penetration Testing (VAPT)
- Web Application Security
- Network & Infrastructure Security
- PCI DSS-Scoped Compliance Assessment
- Engagement Governance & Risk Reporting
- Security Program & Resource Management
From hands-on testing to leading the engagement
A record of the roles that shaped the way I work today — running both the testing and the programme around it.
CyRAACS
Cybersecurity consulting — 4+ years, from hands-on testing to leading engagements.
- Associate ManagerJul 2026 – Present · Bengaluru
- Team LeadJul 2025 – Jun 2026 · Mumbai
- Senior Consultant — Information Security & ComplianceJul 2023 – Jun 2025 · Mumbai · On-site
- Consultant — Technical ServicesMay 2022 – Jun 2023
Freelancer.com
VAPT researcher — independent web application assessments (~9 months).
- VAPT ResearcherAug 2022 – May 2023
Certifications
- CEH (Practical)2024
Certified Ethical Hacker — Practical
EC-Council
- CRTP2025
Certified Red Team Professional
Altered Security
- eWPTX2025
eLearnSecurity Web Application Penetration Tester eXtreme
INE (eLearnSecurity)
Education
- M.S., Cyber Security and Forensics
Southern New Hampshire University
Aug 2024 – Oct 2026
- MBA, Information Technology
Lovely Professional University
Nov 2022 – Aug 2025
- B.E., Computer Science
BMS Institute of Technology and Management
Jul 2018 – Sept 2022
Recognition
- Best Client Recognition
- CyRAACS — Top Performer
- Top 10% on TryHackMe
The tools behind the methodology
Grouped by where they're used across an engagement.
Application & Offensive Security
Network & Infrastructure
Compliance & Governance
Engineering
Principles that shape every engagement
Hands-on offensive experience
Real attacker techniques, applied carefully within scope — not just automated scans and a dashboard.
Structured testing methodology
A repeatable, documented process so every engagement has consistent depth and coverage.
Business-impact reporting
Findings framed around what they mean for your business, not just a list of technical issues.
Clear remediation guidance
Each finding comes with concrete, technically specific steps your team can actually implement.
Confidential handling
Your data, findings, and reports are handled securely and never shared without authorization.
Direct communication
You work directly with the consultant doing the testing — no account-manager relay, no hand-offs.
Flexible engagement models
Point-in-time assessments or an ongoing partnership, scoped to fit your needs and budget.
All testing is conducted only with documented authorization and within an agreed scope. Findings and client information are handled in strict confidence — reach out at freelance@chiragarora.in.
Ready to find your weakest point before an attacker does?
Start with a confidential conversation about your goals and scope. No obligation — just a clear next step toward a more secure product.